
Probably Just Fine - TryHackMe First Shift CTF Writeup
On my first SOC shift, I received an alert about an unusual VPN login from Singapore. The handover notes said the user was traveling, so it seemed normal at first. But the SOC process says to verify everything with threat intel, and this case quickly escalated into a full investigation.
Scenario Summary
- Alert: Unusual VPN login for
susan.martin@probablyfine.thmfrom37.19.201.132(Singapore) - User confirmation: Susan did not log in
- Exposure: She installed a suspicious “security check” prompt on public Wi-Fi
- Host telemetry: A suspicious binary hash
Hash in scope:
b8e02f2bc0ffb42e8cf28e37a26d8d825f639079bf6d948f8debab6440ee5630
Tooling: TryDetectThis
TryDetectThis is the threat intelligence platform used in this room. It lets us check IPs, domains, and hashes to gather context and reputation signals.
URL: https://static-labs.tryhackme.cloud/apps/trydetectthis/
Investigation Walkthrough
Q1: What is the ASN number related to the IP?
We start with the alert IP 37.19.201.132 and search it in TryDetectThis.
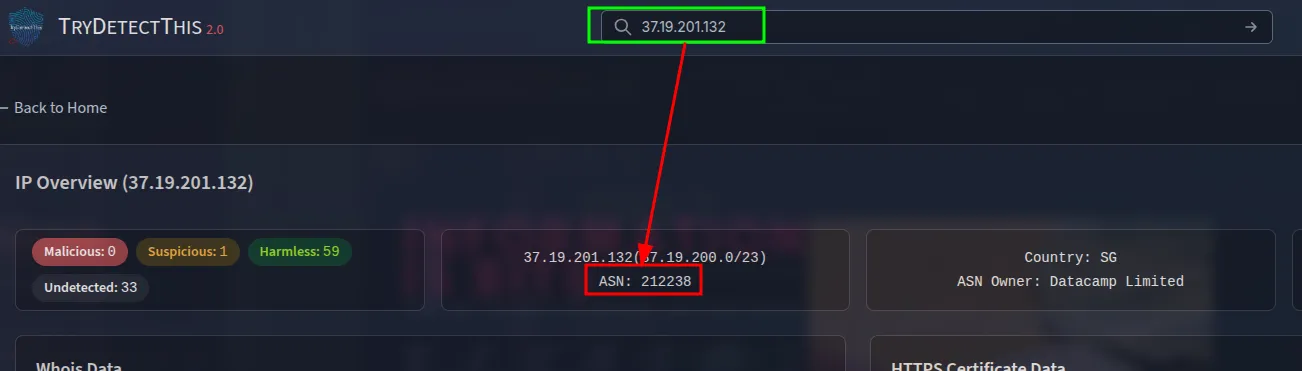
Answer: 212238
Q2: Which service is offered from this IP?
The file relations and infrastructure details point consistently to VPN infrastructure.
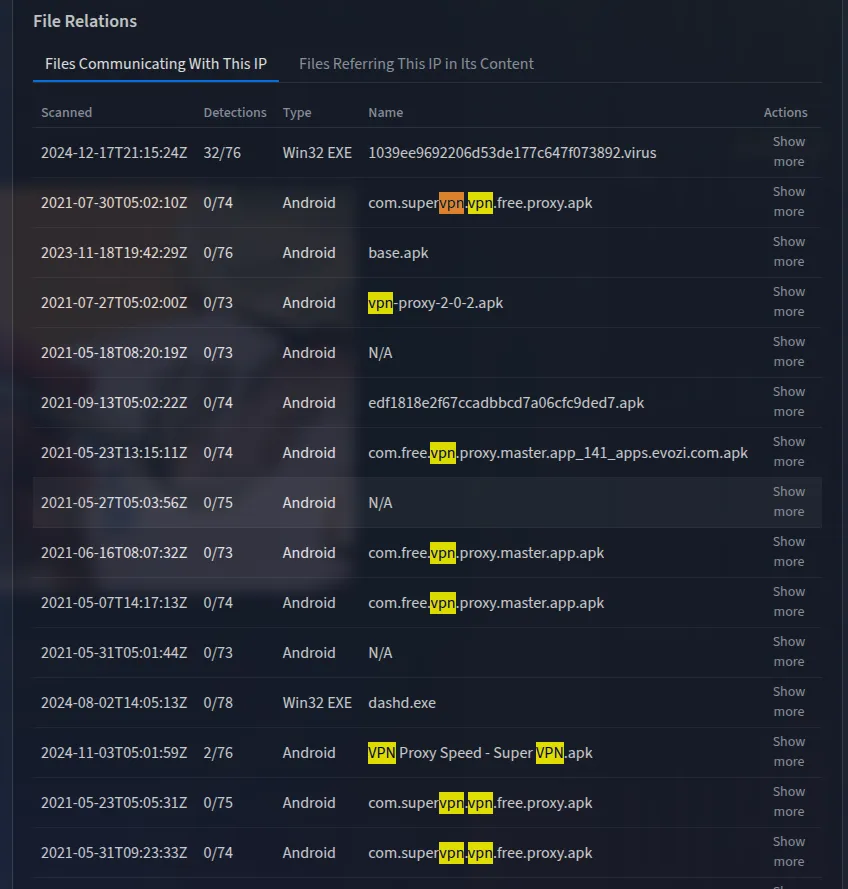
Answer: VPN
Q3: What is the filename of the file related to the hash?
Next, we search the binary hash and review the results.
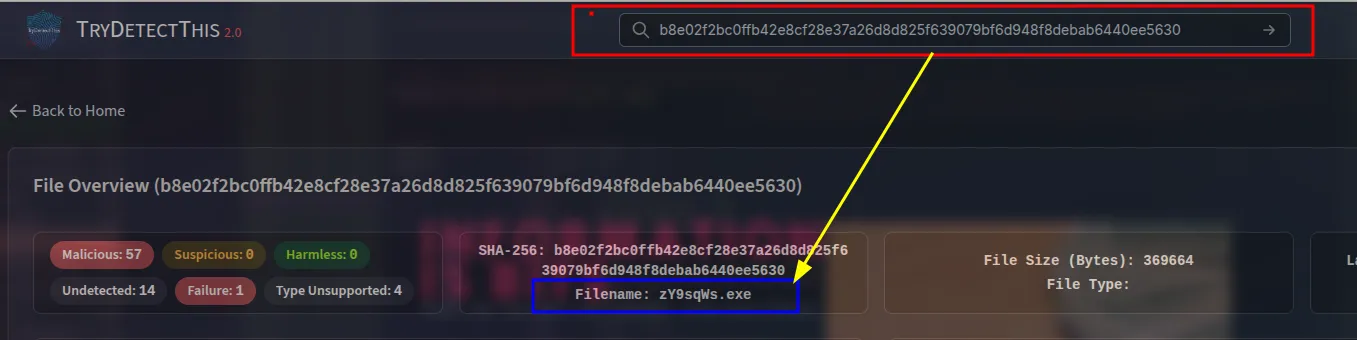
Answer: zY9sqWs.exe
Q4: What is the threat signature that Microsoft assigned to the file?
The vendor analysis section includes Microsoft detections.
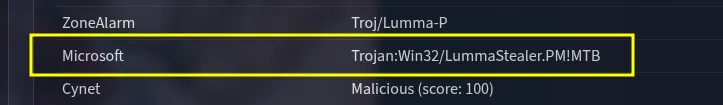
Answer: Trojan:Win32 /LummaStealer.PM!MTB
Q5: Based on the HTTPS certificate, how many domains are linked to the same campaign?
From the contacted domains list, gadgethgfub.icu belongs to a larger infrastructure cluster. Its certificate contains a long list of Subject Alternative Names. Counting the entries yields the total.
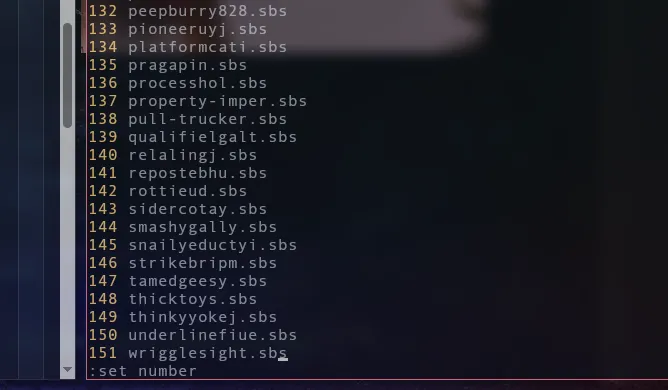
Answer: 151
Q6: What time is present in the YARA rule condition field?
The detection section includes YARA rules authored by kevoreilly. The rule details include the condition field.
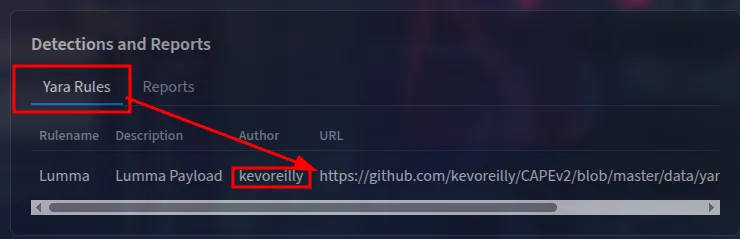
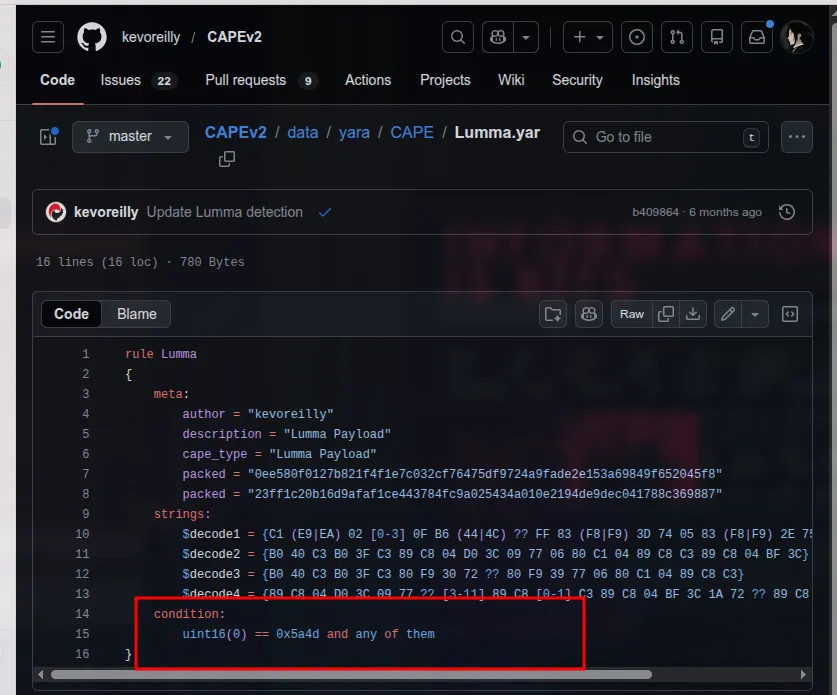
Answer: uint16(0) == 0x5a4d and any of them
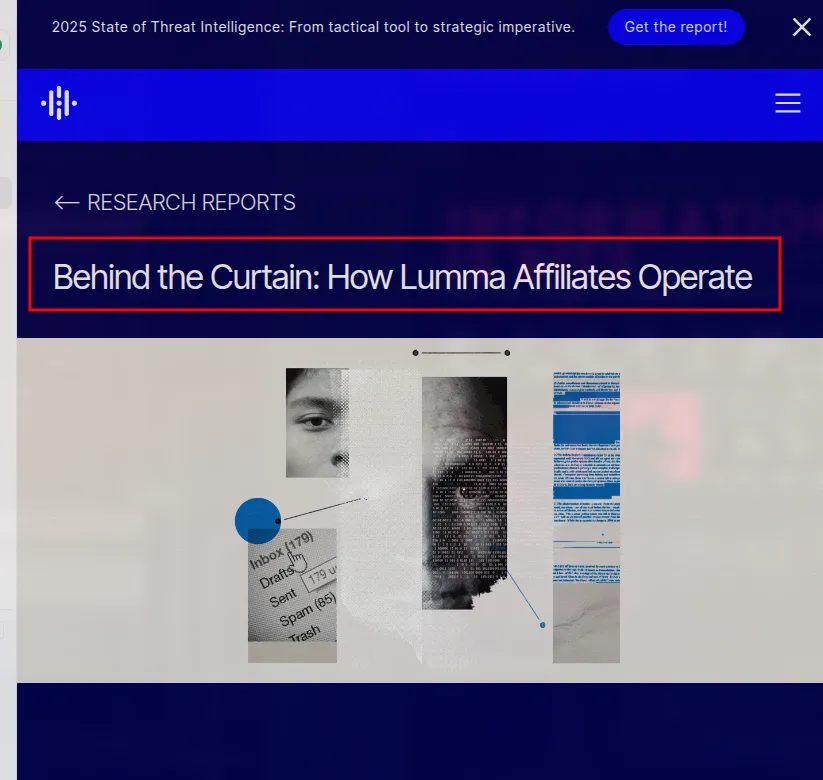
Q7: What is the title of the TI report mentioning this hash?
The same detection section lists reports that reference the hash.
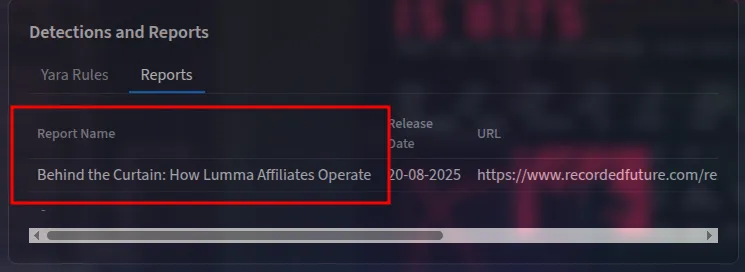
Answer: Behind the Curtain: How Lumma Affiliates Operate
Q8: Which team did the author start collaborating with in early 2024?
The report notes a collaboration in early 2024.
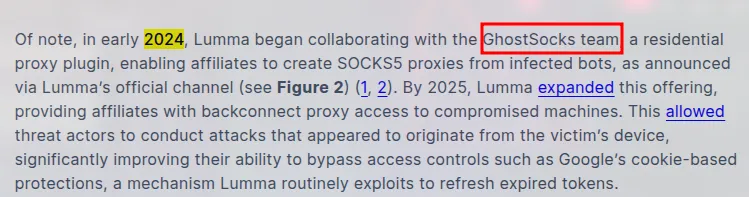
Answer: GhostSocks
Q9: Which mentioned infostealer targets Android systems?
Searching the report for mobile-related references reveals the Android-targeting infostealer.
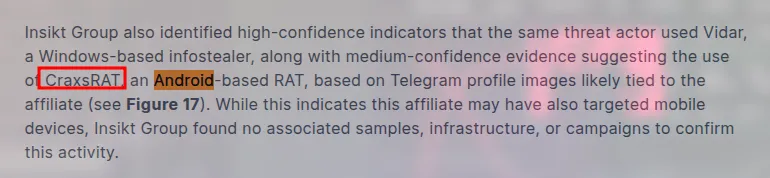
Answer: CraxsRAT
Q10: Which MITRE ATT&CK sub-technique aligns with AnonRDP usage?
The report maps affiliate behavior to MITRE ATT&CK tactics.
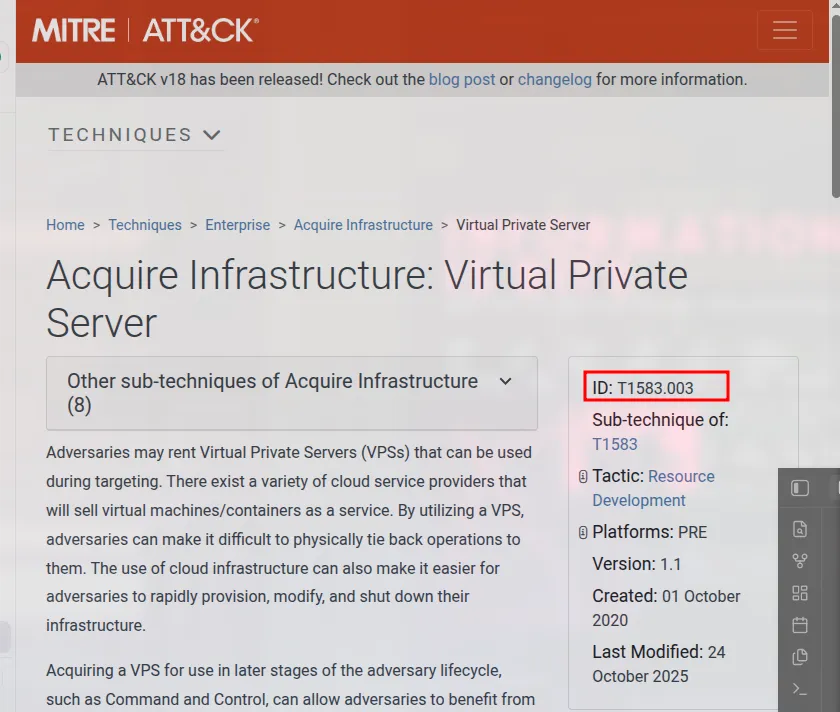
Answer: T1583.003
Key Takeaways
- Threat intel platforms add critical context even when alerts appear benign.
- Hash-based pivots can reveal malware families, infrastructure, and partnerships.
- Reports often answer the hardest questions when raw indicators fall short.
Final Notes
This scenario is a strong example of real SOC workflow: validate, pivot, and document. A single suspicious login quickly expands into a broader picture of malware operations and infrastructure reuse.
Next reads
View all →30 Jan
Cloud Security Pitfalls - TryHackMe Writeup
A friendly, SOC-focused walkthrough of cloud migration risks, shared responsibility, logging challenges, and practical monitoring takeaways.
31 Dec
Mastering Obfuscation Principles - TryHackMe Writeup
A comprehensive guide to understanding obfuscation techniques for malware evasion, from basic concatenation to advanced control flow manipulation. Learn how attackers hide their code and how defenders can spot these techniques.
28 Dec
Understanding the Cyber Kill Chain - TryHackMe Writeup
A comprehensive walkthrough of TryHackMe's Cyber Kill Chain room, exploring each phase of cyber attacks from reconnaissance to actions on objectives, plus a real-world analysis of the Target data breach.
Get posts by email
One email when I publish, not a drip, not weekly. Sign up and I'll only write when there's something new.
You won't get mail just for signing up. Unsubscribe any time.